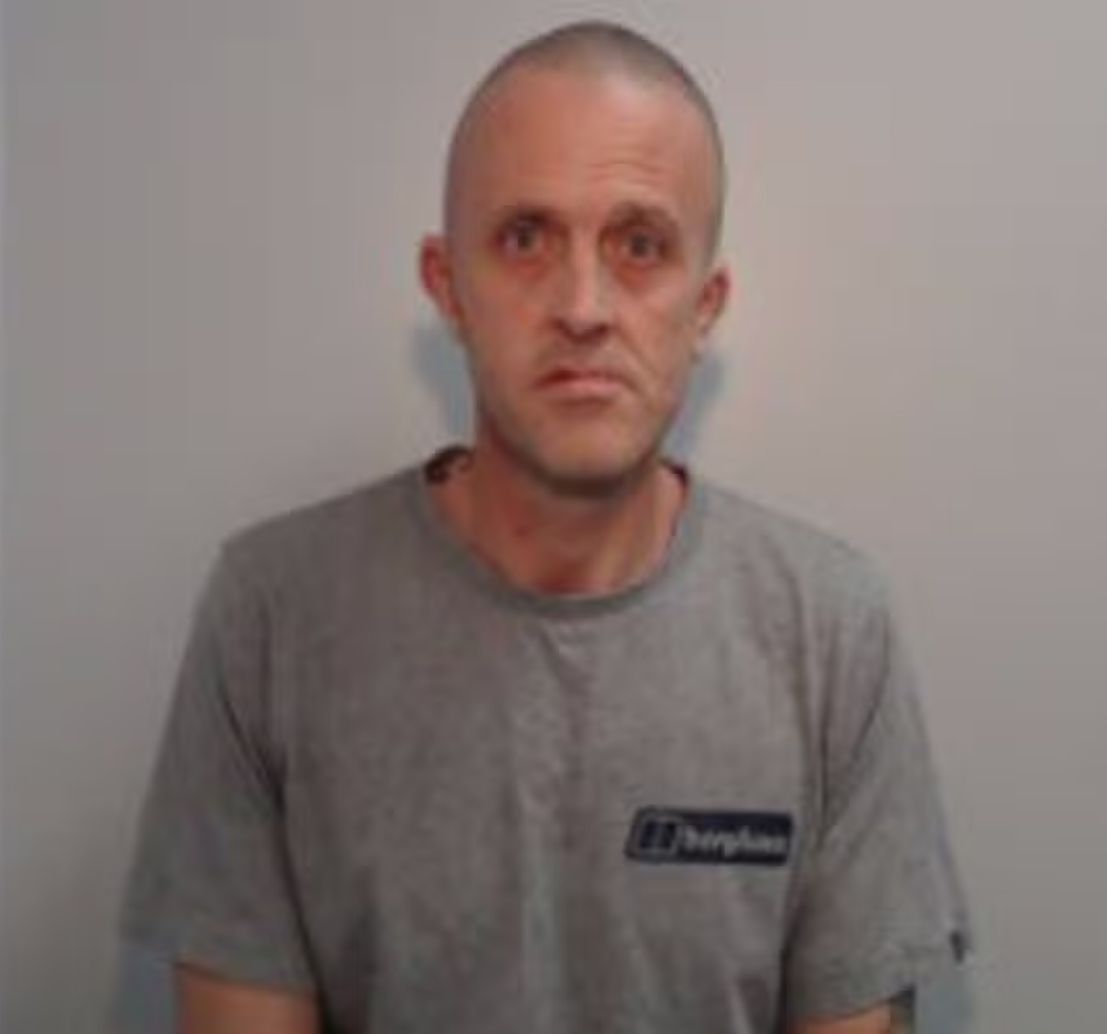
🚨🇬🇧 Dark web child r*pist identified through lingerie photos and images of his hands jailed for 23 years Darren Welsby, 48, was convicted of r*ping and sexually abusing children, some as young as six, and recording and distributing the abuse online. ⠀ Investigators traced Welsby after the username “wellhnug,” used to upload child sexual abuse material on the dark web, was also used on an adult website where he posted photographs of himself wearing women’s lingerie. ⠀ A forensic anthropologist then matched his hands and knuckles to those visible in the abuse images, while digital experts established that the material was captured using one of his phones. A search uncovered more than 30,000 abusive images across 10 devices. Welsby was sentenced to 23 years in prison and will serve a further five years on extended licence. Source: https://www.cps.gov.uk/national-news/news/man-jailed-landmark-conviction-rape-and-child-sexual-abuse
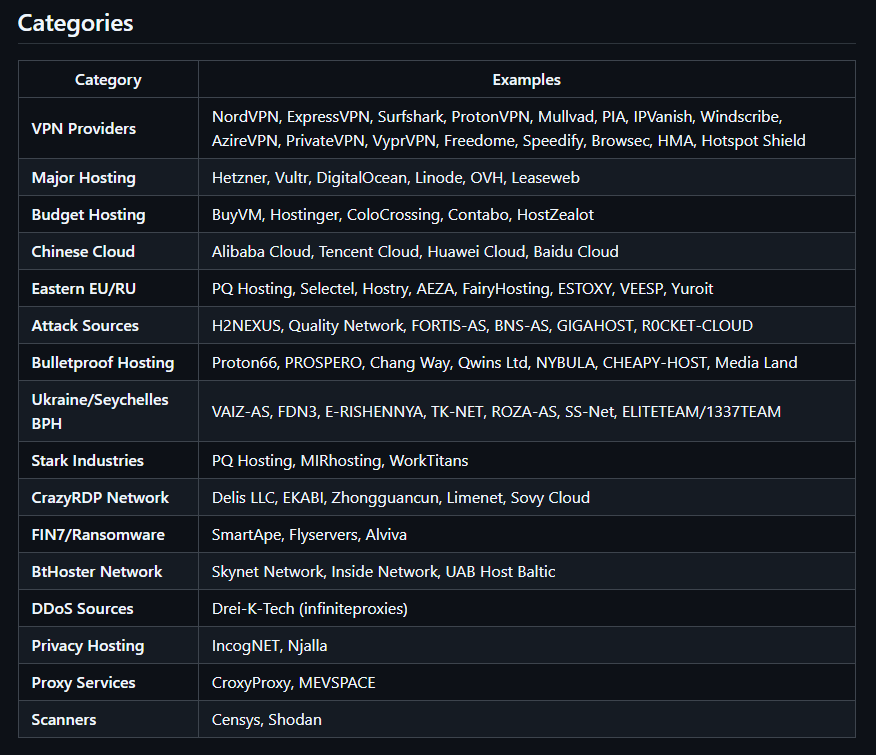
🚨 Bad ASN List: A curated blocklist of 2,200+ ASNs tied to VPNs, datacenters, hosting providers, scanners, and infrastructure commonly associated with automated abuse. GitHub: https://github.com/bountyyfi/bad-asn-list The list is designed to help reduce scraping, credential stuffing, bot traffic, anonymous abuse, and other unwanted activity by identifying suspicious network sources at the ASN level. Includes categories covering: • VPN and proxy providers • Major and budget hosting • Bulletproof hosting • Known scanner infrastructure • DDoS and abuse sources • Infrastructure linked to ransomware and cybercrime activity The repo currently contains 2,234 ASNs and includes implementation examples for Cloudflare Workers, Node.js, Flask, iptables, and nftables.
Per watchTowr on the Citrix situation... - Citrix comms & patches are expected early next week. - Two vulnerabilities - both RCE. Unpatched, 0days. - Exploited in-the-wild - discovered during forensics. https://x.com/DarkWebInformer/status/2103974203548664253
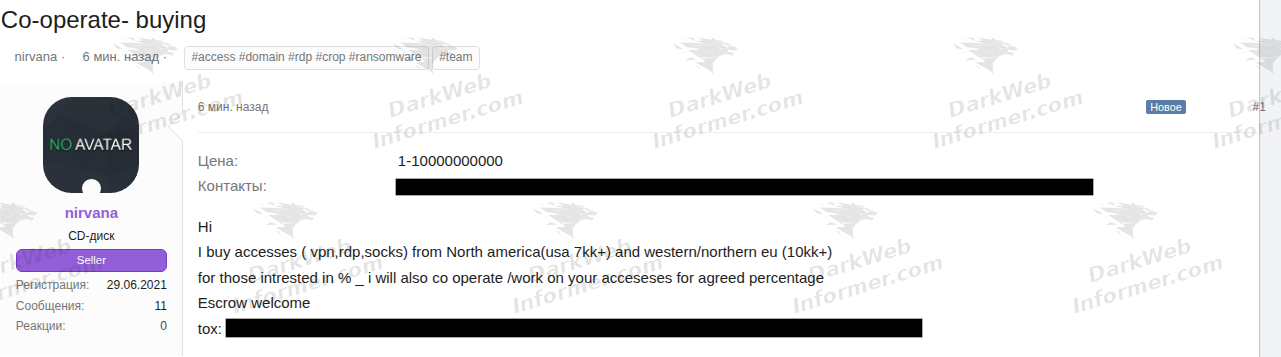
🚨🇺🇸🇪🇺 Actor Seeking VPN, RDP, and SOCKS Access to U.S. and European Networks An actor operating under the handle "nirvana" is looking to purchase unauthorized access to corporate networks across North America and Europe. The listing specifically targets U.S. organizations with a stated threshold of 7 million and companies in Western and Northern Europe with a threshold of 10 million, although the metric is not explicitly defined. The actor is also offering to collaborate with other initial access brokers, proposing percentage-based profit-sharing arrangements for access provided by third parties. Claim is currently unverified. 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
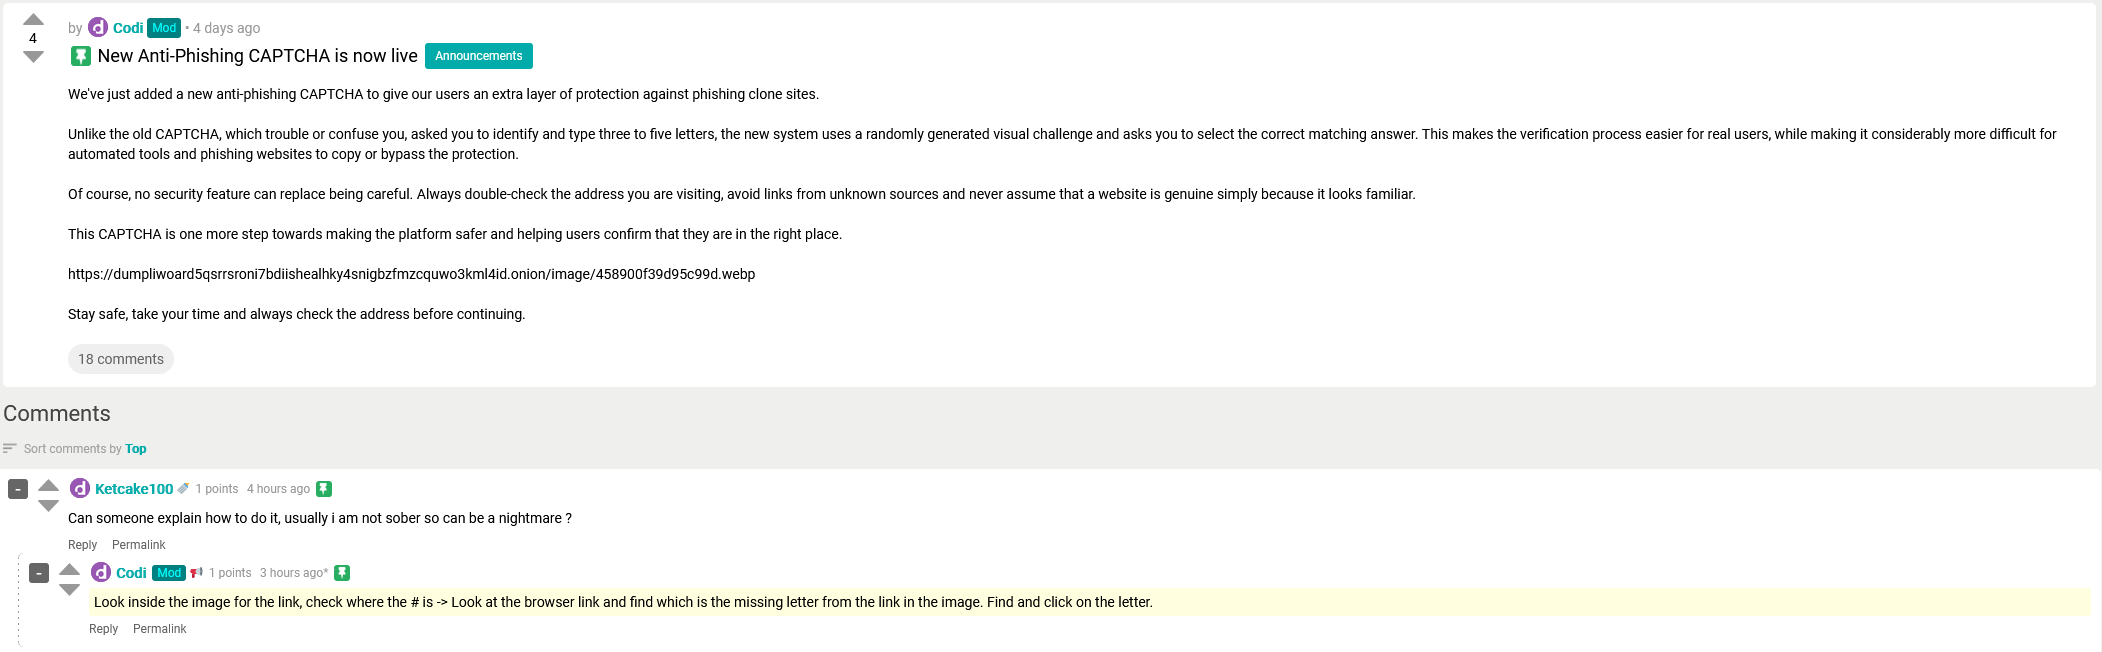
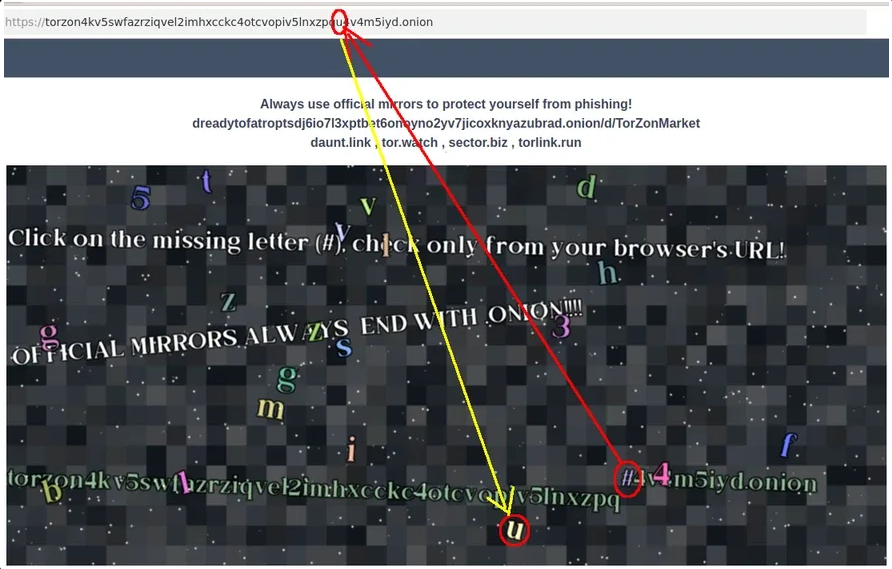
TorZon Market added a new anti-phishing CAPTCHA that asks users to identify a missing letter in the site address, helping verify they are on the legitimate site and not a phishing clone. Dread: https://dreadytofatroptsdj6io7l3xptbet6onoyno2yv7jicoxknyazubrad[.]onion/post/5aa9b314c8f21ebf1113/
🚨 🇫🇷 Plurélya dataset containing public-sector employee and family data offered for $250 ⠀ The actor "ChimeraZ" is selling what they claim is a partial dataset from Plurélya, a French nonprofit that administers social benefits and services for public-sector employees. ⠀ The 4.4 GB JSON archive is advertised as containing 965,575 lines associated with 150,114 people, including 60,245 employees, 89,869 children, and 50,572 records containing account-holder names, BICs, and partial IBANs. ⠀ Samples include names, dates of birth, personal email addresses, home addresses, employment details, internal identifiers, tax-related fields, and records linking employees to their children. The dataset is being offered for $250, payable in Monero. ⠀ The actor also references more than three million identity and tax documents but claims they were detected before obtaining them. It is unclear whether any of those files were accessed or exfiltrated. ⠀ This claim is currently unverified. ⠀ 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
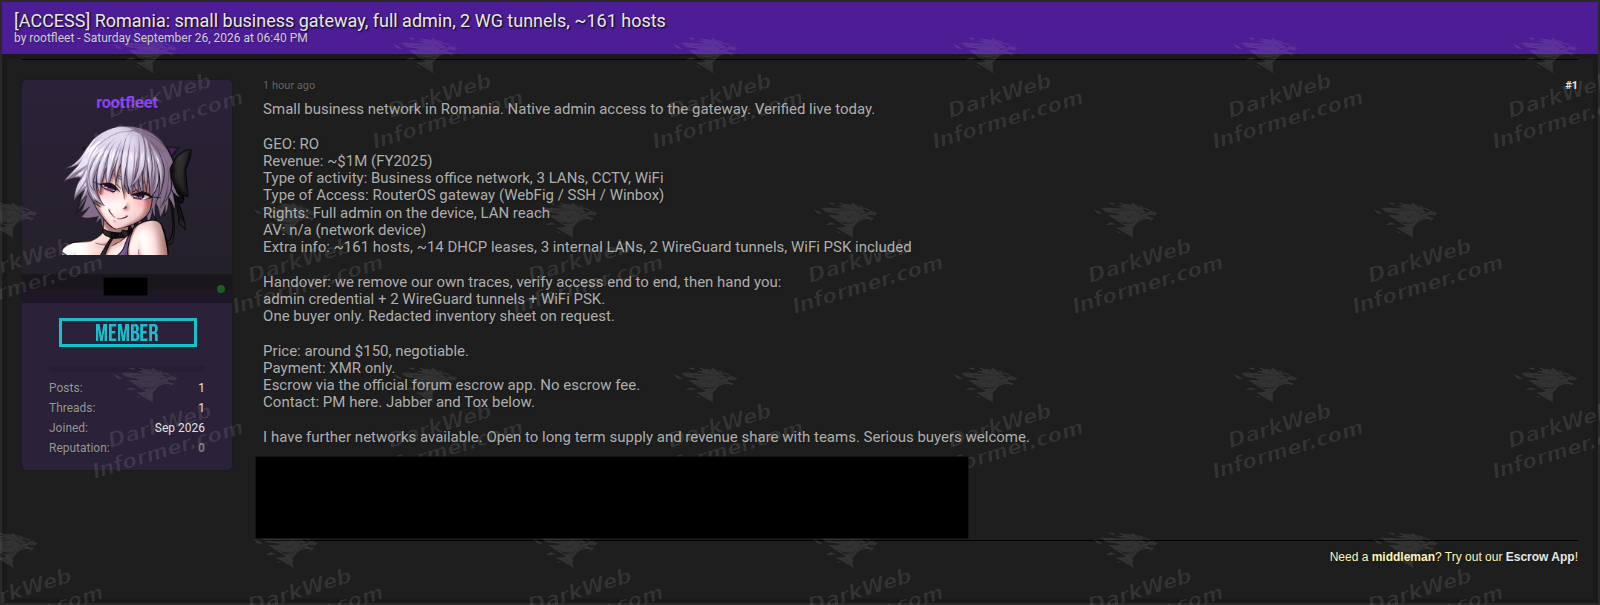
🚨 🇷🇴 Initial Access: Romanian Small Business Network A threat actor is advertising administrative access to an unnamed Romanian business network reportedly generating approximately $1M in annual revenue. The advertised access includes full admin control of a RouterOS gateway, three internal LANs, two WireGuard tunnels, WiFi credentials, and network reach across approximately 161 hosts. The access is listed for around $150 in XMR. This claim is currently unverified. 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
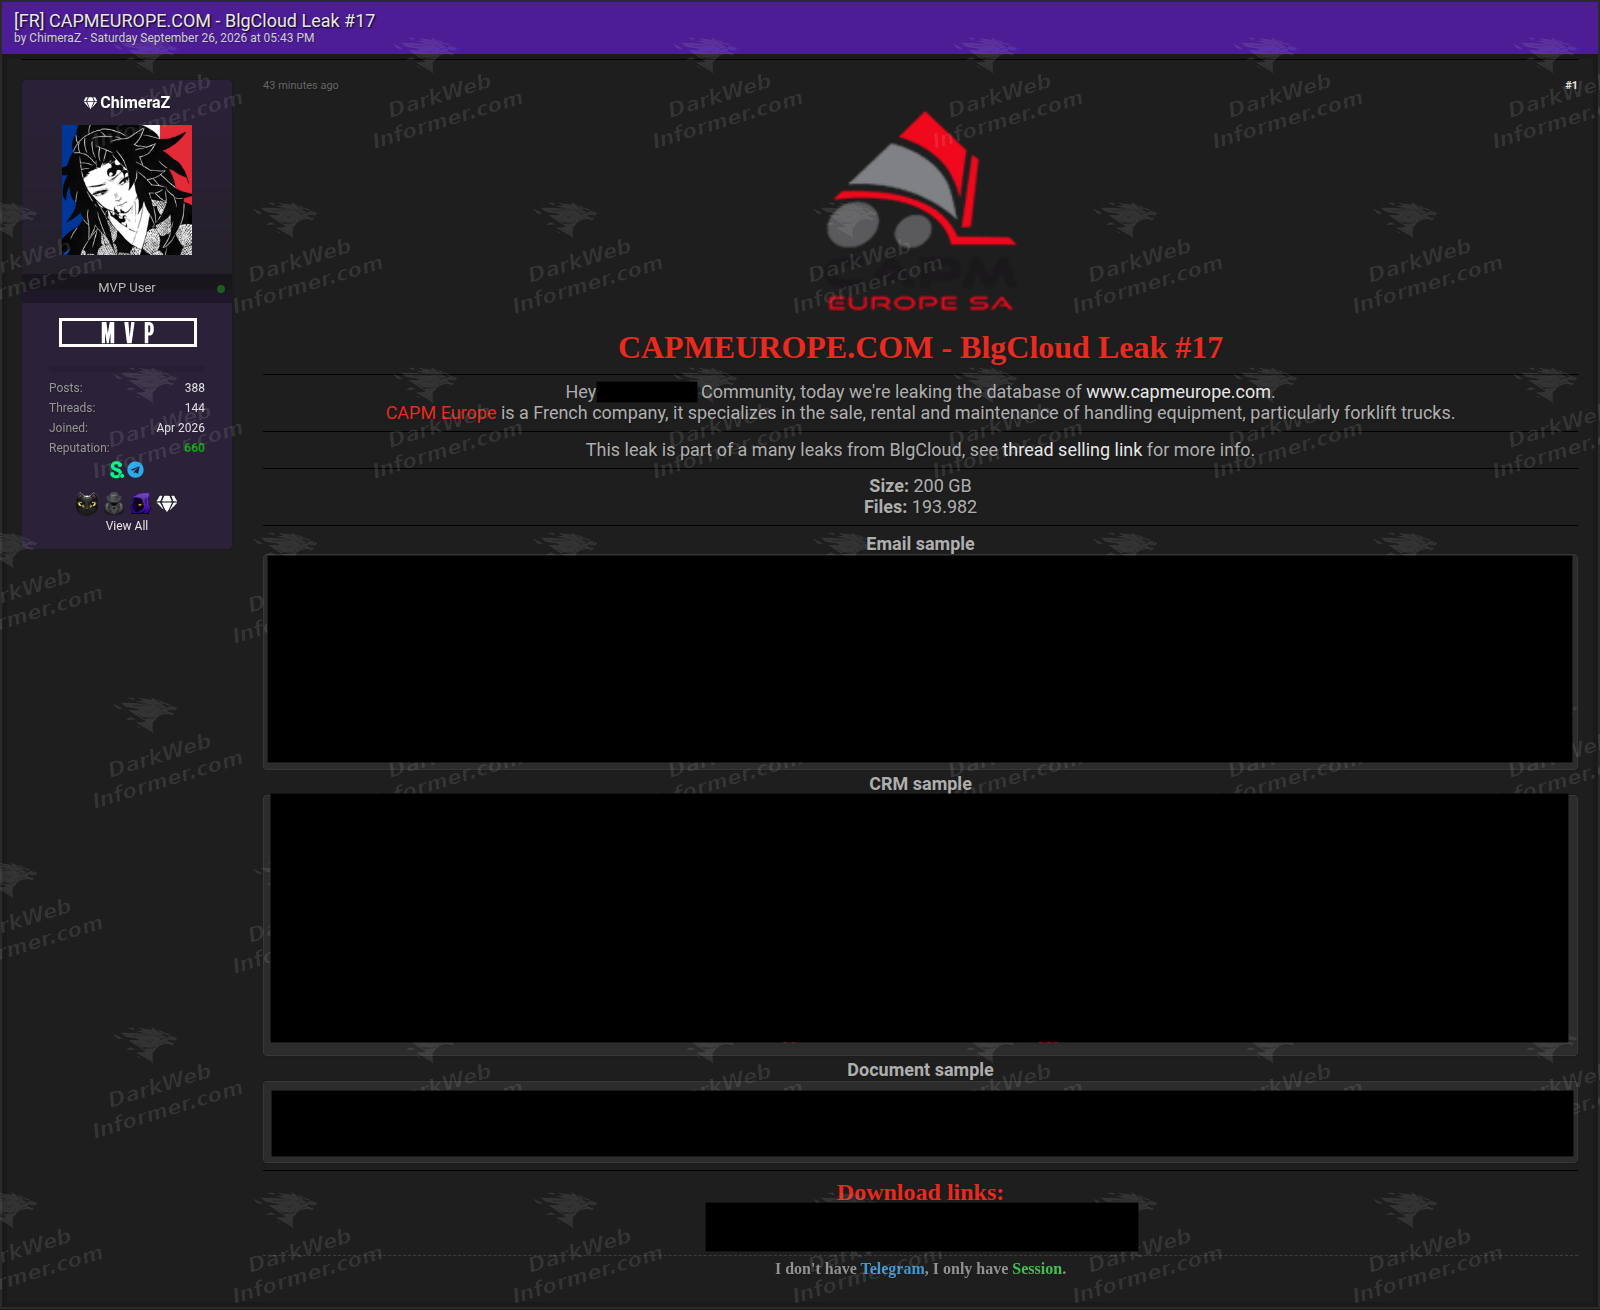
🚨 🇫🇷 200 GB of CAPM Europe data allegedly released in BlgCloud leak series ⠀ The actor "ChimeraZ" has posted download links for data allegedly taken from CAPM Europe, a French company specializing in the sale, rental, and maintenance of forklifts and other handling equipment. ⠀ The archive is advertised as approximately 200 GB containing 193,982 files. Samples shared in the post reference company email, CRM records, and internal documents, including employee and customer contact information, account records, addresses, and document metadata. ⠀ The release is labeled "BlgCloud Leak #17." The post does not explain how CAPM Europe was compromised or when the data was obtained. ⠀ This claim is currently unverified. ⠀ 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
🚨 Companies are being urged to shut down their NetScaler instances immediately due to multiple unpatched Citrix NetScaler RCE vulnerabilities. Source: https://x.com/watchtowrcyber/status/2103891689857228803
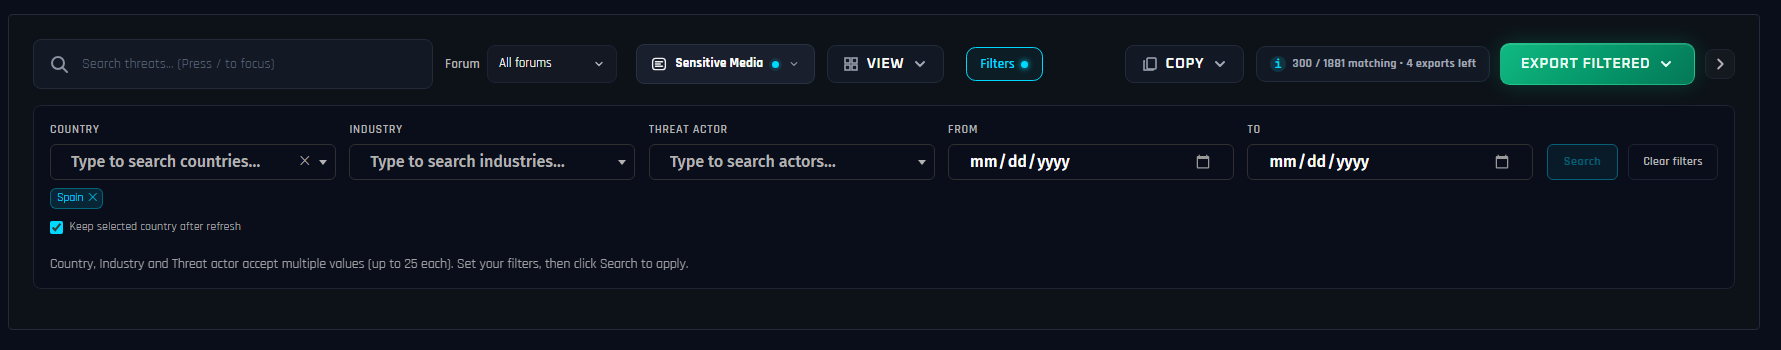
Small Threat Feed update: You can now choose to keep your selected country filter after refreshing the page. For example, select Spain under filters, enable “Keep selected country after refresh,” and it will automatically be restored before the feed loads again. Changing the country updates the saved preference, while clearing filters removes it completely. Also works with multi-country filtering. Refresh the page to get the update.
Welcome to Dark Web Informer :verified_paw: spacestr profile!
About Me
Website: https://darkwebinformer.com Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing Socials: https://darkwebinformer.com/socials API Access: https://darkwebinformer.com/api-details About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer X: https://x.com/DarkWebInformer Updated: 2026-07-20
Interests
- No interests listed.